
KlaritiQKlaritiQ
The KlaritiQ Blog

Rigorous thinking on AI,
from the first model to the final audit.

Technology, governance and traceability, with benchmarks and practical playbooks for Indian companies, written by the team building KlaritiQ.

Latest from KlaritiQ

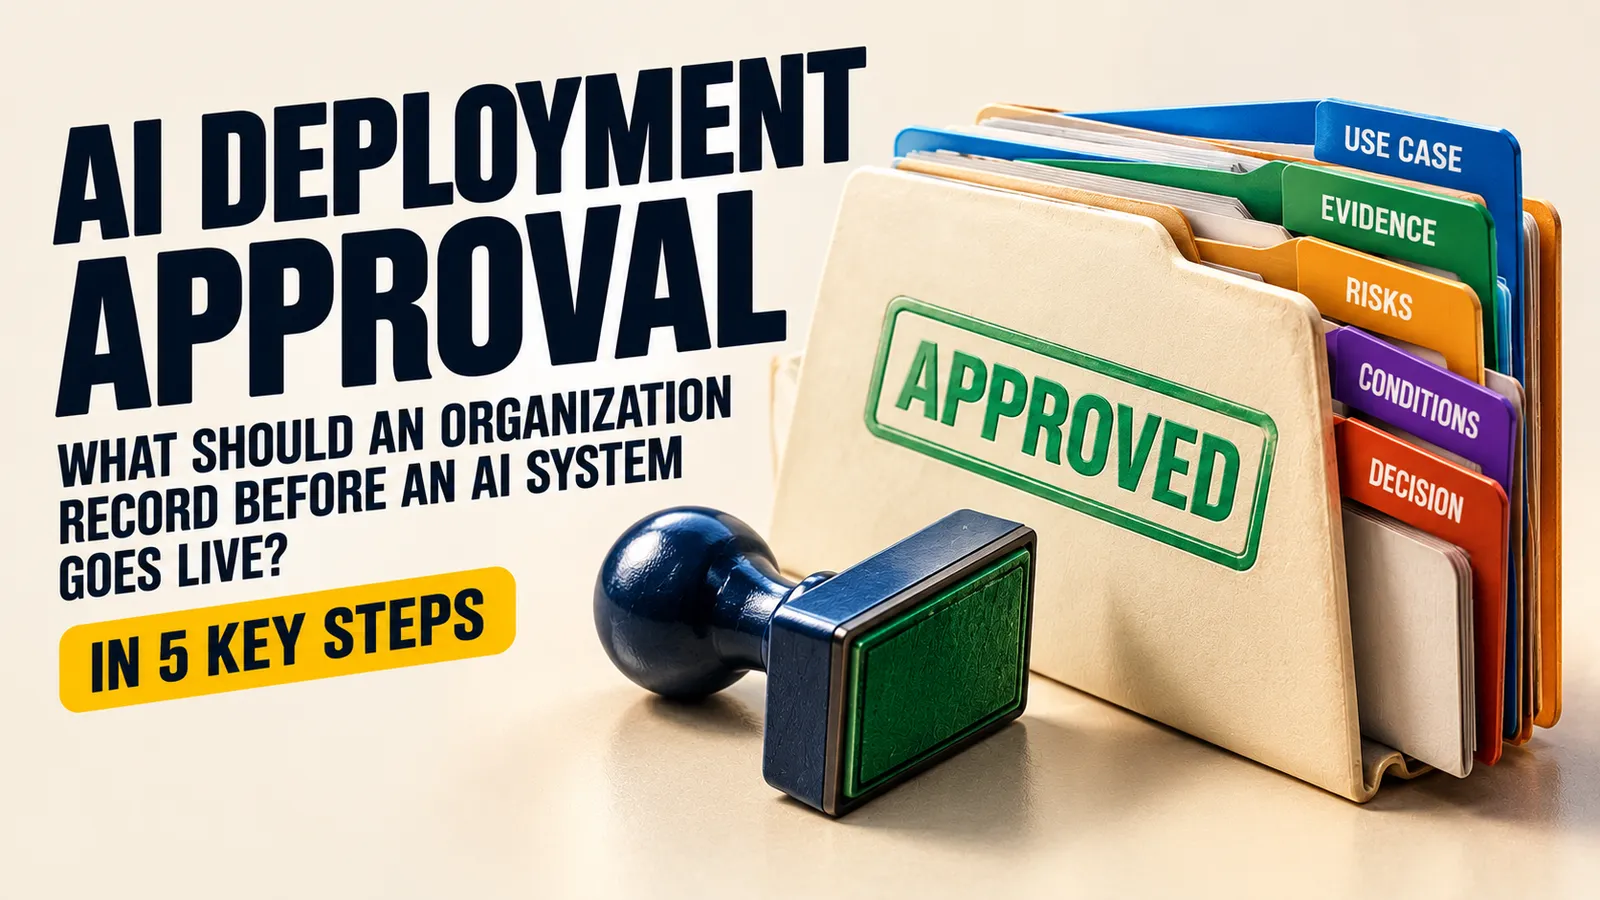
AI deployment approval: what should an organization record before an AI system goes live?

AI deployment approval must connect intended use, supporting evidence, accepted risks, operating conditions and accountable decisions. Continuous AI assurance ensures approvals remain valid as systems, permissions, workflows and risks change.

30 Oct 2026
→

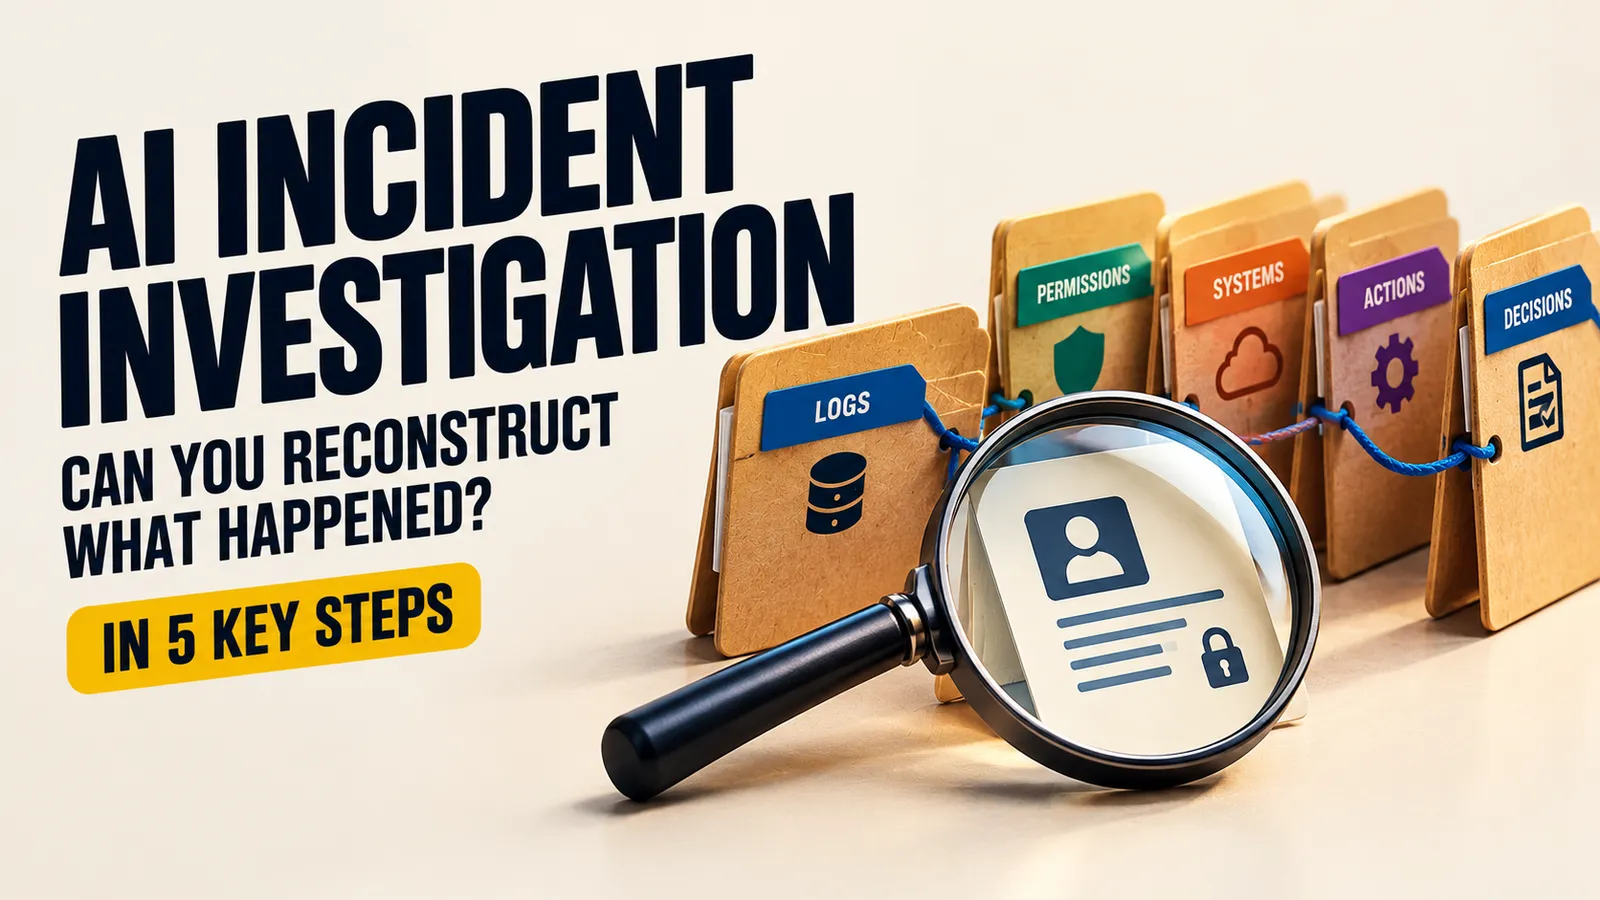
AI Incident Investigation: Can You Reconstruct What Happened?

Investigating AI incidents involving personal data requires reconstructing actions, historical system states, permissions and decisions. Evidence-based assessments, verified remediation and continuous assurance strengthen accountability and support DPDP compliance.

29 Oct 2026
→

AI Incident Reviews: How to Turn Recovery Into Better Controls

An effective AI incident review goes beyond restoring service to uncover root causes, assess wider risks, assign corrective actions, verify fixes and preserve evidence. Clear accountability and continuous assurance help prevent recurrence and strengthen AI governance.

28 Oct 2026
→

AI Agent Authorization: How to Prove What Your AI Was Allowed to Do

AI agents can exceed intended boundaries when permissions are too broad. Enterprises must enforce least privilege, verify access controls, preserve trustworthy activity logs, and continuously connect system changes, approvals, evidence, and accountability.

26 Oct 2026
→

AI Deskilling: How to Protect the Human Expertise Your AI Depends On

AI can boost productivity while quietly weakening the expertise employees need to challenge its mistakes. Learn how to detect deskilling, preserve independent judgment, and build human capability into continuous AI assurance.

23 Oct 2026
→

AI Change Management: How to know whether an AI update is safe to release

AI updates can improve overall performance while weakening critical behaviors. KlaritiQ’s BASE model connects existing risks, corrective actions, decisions and evidence to help organizations evaluate changes, maintain accountability and reassess whether approvals still hold.

20 Oct 2026
→

AI Inventory Management: How to make AI inventory management useful when a system changes, fails, or comes under investigation

AI inventories can become outdated as models, permissions, integrations and workflows change. During an incident, stale records leave teams uncertain about potential exposure, dependencies and containment decisions. This article explains how to build incident-ready inventories, verify evidence and ownership, test response procedures, and connect AI inventory management to continuous assurance.<

19 Oct 2026
→

AI Agent Access Control: How to prevent excessive permissions and unintended actions

Approved tools can create unintended outcomes when combined. Map tool-to-tool workflows, constrain actions by task and risk, enforce independent controls, test failure scenarios, and reassess permissions whenever capabilities change.

15 Oct 2026
→

AI agent security: what should organizations do when an agent takes an unintended action?

As AI agents gain access to enterprise systems, unexpected actions are becoming an operational risk. Salt Security’s research highlights gaps in traceability and containment. Organizations need to distinguish operational errors from control failures and security incidents, reconstruct events across systems, assess impact, assign corrective actions and verify outcomes. Detection alone is not ass

14 Oct 2026
→

Internal Controls Testing: Can Your Controls Miss Failures and Still Pass?

Internal controls can pass testing while still missing failures if the tested sample is unrepresentative, parts of the population are excluded, or monitoring systems fail to capture relevant activity. Organizations need complete population records, automated exception detection, monitoring reconciliation and independent testing to verify that controls work as intended and gaps are investigated.

12 Oct 2026
→

AI Decision Traceability: What You Need to Know About an AI Decision After It Happens

AI systems change constantly, but most governance records capture only what happened, not the exact system state behind a decision. This article explains why AI decision logging must connect decisions with model versions, data, configurations, dependencies, controls, and evidence, enabling organizations to reconstruct what their AI actually was when consequential decisions occurred.

8 Oct 2026
→

AI Vendor Risk Management: What Happens When Your AI Vendor Changes the Model?

AI systems can change without internal deployments through model upgrades, vendor updates, data changes, APIs, dependencies, or permissions. The governance challenge is determining whether those external changes materially affect risk, existing approvals, ownership, and evidence. The enterprise ultimately remains accountable for continuing to operate the changed system. 

6 Oct 2026
→

Your AI Has Git. Your Governance Doesn't.

AI systems have version control, but governance often doesn’t. Engineers can reconstruct exactly what changed, while governance may only show an old approval disconnected from the system that actually ran. The article argues for versioned, state-aware governance that links AI changes, approvals, evidence, and decisions over time.

5 Oct 2026
→

Your Compliance System Says “Compliant.” Can You Prove It?

Having a written policy or a green "Compliant" dashboard does not mean your organization is actually compliant; the true test lies in whether you can readily prove how a control operated in practice

23 Sept 2026
→

The AI Employee Nobody Put on the Org Chart

Your AI keeps changing after you approve it. Monitoring shows what changed, not whether that approval still holds. That gap is the real risk.

9 Sept 2026
→

Point-in-Time vs Real-Time AI Assurance: Why Your AI Can Be “Compliant” and Still Be at Risk

Point-in-time assurance tells you whether an AI system met requirements when it was assessed. Real-time monitoring tells you what is changing as the system operates. Neither is enough alone. Modern AI assurance connects the two: detect what changed, understand its impact, make an accountable decision, take action, and preserve the evidence to prove what still holds.

2 Sept 2026
→

Why AI Deployment is Only Half the Battle (And Why Static Governance Fails)

While 70% of organizations deploy AI, only 2% run it maturely. Live systems constantly change as datasets drift and models update. Static, point-in-time assessments cannot track these shifting conditions

19 Aug 2026
→

Why KlaritiQ Exists: Building the Future of Continuous AI Assurance

KlaritiQ is a Continuous AI Assurance platform that helps organizations know what is true at any moment. By continuously governing evidence, policies, controls, vendors, AI initiatives, and organizational dependencies, KlaritiQ produces defensible assurance that enables leaders to make decisions based on verified reality rather than assumptions.

3 Aug 2026
→

The Examiner Who Never Sleeps: Why Annual Audits Are Just Security Theater

Annual audits create a 363-day blind spot where hidden compliance risks accumulate. Under regulations like India's DPDP Rules 2025, continuous AI governance replaces staged, once-a-year "security theater" with real-time, automated protection.

27 Jul 2026
→

The Keystroke That Destroys Your Compliance: Are You Governing or Just Excavating?

A mistake takes 3 seconds. Your review process takes 3 weeks. By the time you spot the breach, the damage is already done and the bill is in the mail.

21 Jul 2026
→

The Form Is an Apology: Why Enterprise Questionnaires Are Obsolete

Every compliance questionnaire is a workaround for a machine that couldn't read. The machine can read now. Learn why evidence-based verification is replacing self-reported risk assessments under DPDP.

20 Jul 2026
→

The Pilot Paradox: Why 80% of Mid-Market AI Initiatives Stall After the Demo

Most corporate AI pilots stall when they encounter the three pillars of operational deployment: data lineage, cross-functional accountability, and governance (DPDP). The bottleneck is no longer capability; it’s operational discipline. Learn how to br

15 Jul 2026
→

AI Readiness Assessment: The Complete Enterprise Guide (2026)

Learn how to measure your organization's AI readiness across strategy, people, data, infrastructure, and governance. Includes a free AI Readiness checklist and enterprise framework.

10 Jul 2026
→

The Anatomy of a 45-Hour Migration: Consolidating Departmental Chaos Into One Hub

Stop automating chaos. Migrating messy data into a new platform just builds an expensive version of legacy debt. To win, spend 10h on architecture, 20h on config, and 15h testing. Map first, build second.

3 Jul 2026
→

The Process Debt Trap: Why New Software Can’t Fix Broken Workflows

Most digital transformations fail because of broken processes, not bad software. Technology only accelerates existing workflows, so automating inefficiency creates faster chaos. Map and simplify your processes first, then configure the software.

2 Jul 2026
→

Why your Enterprise AI stalls at the Database: The hidden lineage crisis in Indian tech architecture

70% of Indian AI projects stall. It's not your prompts, your models, or your tech team. The real culprit is a hidden, multi-core "data lineage crisis" rotting inside your legacy architecture.

26 Jun 2026
→

The AI skills gap in India: it's not about Coding

Indians fear AI will replace them. But the real gap isn't technical it's leadership, judgment, and understanding. Here's what actually matters.

25 Jun 2026
→

While Europe builds rulebooks, India is building runways

The winners of the AI decade won't be the companies with the biggest models. They'll be the countries that let builders move fast without abandoning trust. Because speed without trust creates hype, but trust creates empires.

23 Jun 2026
→

The ₹250 Crore AI Mistake Most Indian Companies Won't Discover Until It's Too Late

DPDP Act means compliance is no longer a legal afterthought; it's the absolute foundation of your architecture. If your data isn't clean enough to satisfy regulatory parameters, it's too weak to power an AI model.

22 Jun 2026
→

Why AI Adoption Fails? (And How to Fix It)

70% of corporate AI projects collapse into expensive, silent failures. But studying why they die reveals an uncomfortable truth: the breakdown isn't caused by the complexity of the technology, but by the cracks in our own human alignment.

21 Jun 2026
→
Featured
10-minute read · Benchmarks

India's MSME digital maturity sits at 58 out of 100.
Here's what that actually means.

Published India research, the MSME Digital Maturity Index (Vi Business, 2025) and CII-KPMG's manufacturing data, tells a consistent story: maturity is early-stage but rising, and the gap between AI ambition and execution is wide enough to matter.

AT
KlaritiQ Team
Research & Insights
June 10, 2026
10 min read
India Avg · ARI Score
64
Contender
Strategy
72
People
60
Data
58
Infra
55
Gov
38
All articles
🧠
People & Literacy

Your AI strategy will fail without this one hire first

An internal AI champion is the most reliable predictor of adoption in Indian mid-market firms, more than budget or headcount. Here's the job description you actually need.

June 5, 2026 · 7 min
→
🗄️
Data Foundations

Why "we have data" is not the same as "we're data-ready for AI"

Indian companies consistently overestimate their data readiness. Here are the four failure modes that block AI value, and how to fix them in 30 days.

May 28, 2026 · 8 min
→
⚖️
Governance

India's AI governance gap is a business risk, not just an ethics issue

With DPDP Act implementation underway, governance is suddenly not optional. Companies scoring below 50 on ARI's governance dimension face concrete compliance exposure. Here's what to build first.

May 20, 2026 · 9 min
→

New posts, straight to your inbox.

Real numbers from real assessments, how Indian companies are moving on AI maturity, which industries are accelerating, and what the top 10% are doing differently. We email you the moment a new post goes up, nothing more.

58
India MSME maturity · Vi Business 2025
Benchmarks

Where India actually stands on AI readiness, and the gap that defines 2026.

AT
KlaritiQ Team
Research & Insights
June 10, 2026
10 min read

When we built KlaritiQ, we started from a hypothesis: most Indian companies believe they are further along on AI than they actually are. The published research backs it up, with one important nuance. (For how we turn that into a single comparable number, see how the AI Readiness Index is calculated.)

India's MSME Digital Maturity Index sits at about 58 out of 100 (Vi Business, 2025), and only 12% of MSMEs reach full digital maturity. For mid-size manufacturers specifically, CII-KPMG puts maturity at 2.9 out of 5, early-stage but real. Not laggards, but not leaders either.

What "early-stage but real" looks like

It usually means a company has done several things right: leadership has named AI a priority, a pilot or two is running, someone owns a roadmap on paper. The gap is rarely ambition, it's execution.

The defining pattern of 2026 is the intent-execution gap. Surveys show roughly 94% of firms recognise AI's value and around 72% plan to increase cloud spend, yet only about 28% of manufacturers had reached meaningful AI adoption by FY24 (TeamLease). Intent is rising faster than execution.

Companies are building on a foundation they haven't finished constructing, making AI announcements while data quality and governance go unaddressed beneath the surface.

Where the real gaps are

58
National MSME maturity (/100)
Vi Business, 2025
2.9
Mid-size mfg maturity (/5)
CII-KPMG
~28%
At meaningful AI adoption
by FY24 · TeamLease

Talent is the binding constraint. ML, data-science and architect roles run a 60–73% demand-supply gap in India, and a data scientist costs ₹12–28 LPA fully loaded. For most mid-market firms, hiring a team for a first project is costly and high-risk, buying or renting capability beats building it.

Data is the under-counted bottleneck. Companies report having "a lot of data," but volume isn't readiness. Data preparation alone is 30–60% of an AI project's cost, the single most under-budgeted line item.

Build-vs-buy is where budgets are won or lost. Purchased or partnered AI tools succeed roughly 67% of the time; first-time internal builds succeed about a third as often (~22%, per NANDA, research with varying success definitions). Moving a custom build from proof-of-concept to production raises cost 250–400%.

Governance is the most urgent gap. With the DPDP Rules gazetted in November 2025 and core obligations enforceable from May 2027, 2026 is a build year, not a grace period. Using existing personal data for a new AI purpose requires fresh consent, and liability stays with you even when the AI is an outsourced tool.

What separates the movers from the stuck

Three moves consistently mark the firms that pull ahead:

  1. Name an owner. A single accountable person for AI, policy, data, and a first use case, beats a committee. Enthusiasm without a mandate stalls.
  2. Fix data before models. Audit the data behind your top use case first. Most stalled initiatives are blocked by data problems, not model problems, and data prep is where the cost hides.
  3. Buy or rent your first win. At this scale, off-the-shelf SaaS or a managed API gets you a working result faster and cheaper than building, and lets you prove value before committing.

Want to see where your company sits? The full ARI assessment is one sitting, under 8 minutes, and gives you a tier for every dimension, the weakest one named, and a concrete 90-day plan.

🧠
People & Literacy

Your AI strategy will fail without this one hire first

AT
KlaritiQ Team
Research & Insights
June 5, 2026
7 min read

One variable predicts AI success in Indian mid-market firms more reliably than budget, headcount, or the number of AI tools deployed: the presence, or absence, of a dedicated internal AI champion.

It's a pattern that repeats. The firms that move have a named, empowered champion driving adoption; the ones that stall have enthusiasm spread across a committee and owned by no one. Against a talent market where ML and data-science roles run a 60–73% demand-supply gap, an internal owner who can direct AI, rather than an expensive new specialist hire, is often the difference between a pilot that ships and one that quietly dies.

What an AI champion actually does

This isn't a data scientist. It's not the CTO doubling as "the AI person." It's a dedicated operator, someone whose explicit job is to drive AI adoption across the organization, not ship models.

  1. They speak both languages, engineering and business, without code-switching between teams.
  2. They run toward the messy organizational problems rather than deferring to later.
  3. They can identify a 90-day quick win, execute it, and tell the story in a board meeting.
  4. They have a personal conviction about AI that isn't easily eroded by setbacks or skeptics.

The job description you actually need

Title: Head of AI Enablement (or VP of AI / Director of AI Transformation)

Reports to: CEO or COO (not CTO, this role is cross-functional, not an engineering sub-team)

Success metric at 90 days: One production AI deployment that non-technical stakeholders can point to, explain, and measure.

What they're responsible for: Identifying high-value AI use cases across departments. Running the internal AI literacy program. Coordinating between data, engineering, legal, and business units. Tracking the company's ARI score over time.

What they are not responsible for: Building models. Managing the data platform. Generating R&D output. Those are engineering functions. Mixing them with the champion role is how organizations burn out good people.

If you can't hire yet, name someone

Early-stage companies often can't make a full-time hire immediately. The fallback isn't to leave the chair empty, it's to formally name an existing team member as the AI champion, with 20–30% of their time and explicit mandate. Our data shows that even a part-time champion, with real authority, produces measurable ARI improvement within one quarter.

Curious how your team scores on the People & Literacy dimension, and what your biggest gaps look like? Run the KlaritiQ assessment and get a dimension-by-dimension breakdown in a single sitting.

🗄️
Data Foundations

Why "we have data" is not the same as "we're data-ready for AI"

AT
KlaritiQ Team
Research & Insights
May 28, 2026
8 min read

The most common thing founders and CTOs say when we start a KlaritiQ assessment: "Our data situation is pretty good, we've been collecting it for years." And then the Data Foundations dimension scores come back, and the conversation changes.

Across Indian mid-market firms, the bottleneck is data readiness, not data volume. Companies have enormous datasets; what they lack is data that's owned, clean, and accessible to a model. Volume and readiness are completely different things, and the gap is expensive: data preparation alone runs 30–60% of an AI project's cost, the single most under-budgeted line item.

The four failure modes we see in every assessment

1. No data ownership

Data that "belongs to everyone" belongs to no one. Without a named owner for each key data domain, there are no quality standards, no update cadences, and no one to call when an ML model starts behaving strangely because its training data drifted.

2. No data lineage

Can your team answer: "Where did this column come from, and what transformations has it been through?" If not, you can't trust what you'd use to train a model. Lineage is the chain of custody for data.

3. Siloed systems that can't talk

The data is in three CRMs, two data warehouses, an old MySQL database from 2019, and three different BI tools. Each team's definition of "a customer" is slightly different. This isn't a ML problem, it's a data architecture problem that blocks ML entirely.

The optimism is understandable, and usually misplaced. When you probe the specifics, ownership, lineage, quality gates, accessibility, most companies that rate their data as "good" have at least two of these four failure modes present. The same pattern shows up in enterprise software, where roughly 75% of ERP implementations get derailed, and the root causes are organisational, not technical. The gap is solvable, but only once it's visible.

4. No quality gates in the data pipeline

Data enters the system and nothing validates it. Duplicate records, null values in critical fields, schema drift from upstream API changes, these compound silently until they surface as a model that starts making confidently wrong predictions.

The 30-day fix that changes the trajectory

  1. Pick one use case. Identify its three core data inputs. Don't generalize. What data, specifically, would this model consume?
  2. Run a data quality audit on those three inputs. Completeness, accuracy, consistency, timeliness. Measure it. Quantify the gaps.
  3. Assign an owner to each data domain. One person. Accountable. In writing.
  4. Add one quality gate to the pipeline. A dbt test, a Great Expectations check, an anomaly alert in your warehouse. One gate, running in production, before you train anything.

Get a precise score on your Data Foundations dimension, plus a prioritized plan to close the gaps before they block your AI roadmap.

⚖️
Governance

India's AI governance gap is a business risk, not just an ethics issue

AT
KlaritiQ Team
Research & Insights
May 20, 2026
9 min read

When governance comes up in an AI readiness conversation, the default reaction from founders and product teams is a kind of respectful dismissal. "Yes, we'll get to that." In 2026, that posture is a business risk.

The numbers

Nov 2025
DPDP Rules gazetted
the build year has started
May 2027
Core obligations enforceable
possibly Nov 2026 if accelerated
100%
of liability stays with you
even when AI is outsourced

Three concrete risks that land on your P&L

1. DPDP Act compliance

India's Digital Personal Data Protection Act is not a future consideration. AI systems that process personal data require data principal consent frameworks, breach notification protocols, and data fiduciary obligations. Companies without governance infrastructure aren't just ethically exposed; they're non-compliant.

2. Enterprise customer requirements

If your company sells to mid-market or enterprise customers, AI governance questionnaires are now standard in vendor security reviews. Customers are asking: Do you have an AI usage policy? Do you conduct bias audits? Without answers, deals stall or don't close.

3. Model failure liability

When an AI system makes a consequential error, the question immediately becomes: what oversight was in place? Companies with governance frameworks have an answer. Companies without one have exposure.

What to build first (the minimum viable governance stack)

You don't need a 40-page AI ethics charter to close the gap. You need three artifacts that can be written in one intensive week: a responsible AI policy, a model risk assessment template, and an AI inventory.

The Responsible AI Policy (2–4 pages): What AI systems are you building or using? What decisions do they inform? What are the prohibited use cases? Who reviews AI systems before deployment?

The Model Risk Assessment Template (1 page per model): What data does this model use? What's the failure mode? Who monitors it in production? When was it last audited?

The AI Inventory (spreadsheet is fine): A list of every AI tool or model in use across the company, including the third-party SaaS tools with embedded AI features that most companies forget about entirely.

The 90-day governance sprint

A focused 90-day governance sprint, write the policy, complete the inventory, run one model risk assessment, is enough to move a firm from improvising compliance on every project to a defensible baseline. And for an ordinary mid-market manufacturer, the heaviest obligations (like algorithmic due diligence, which bites only on notified significant data fiduciaries) don't even apply yet. That's exactly why the build year is the cheap time to act.

See your governance score specifically, and get a prioritized action plan that targets your weakest governance gaps first.

The KlaritiQ Blog· 30 Oct 2026

AI deployment approval: what should an organization record before an AI system goes live?

The important question before an AI system goes live is not simply whether the required documents exist. It is whether the organization can explain exactly what it has approved, what evidence justified that approval, and the conditions under which the approval remains valid.

A model card can describe a model's limitations. A security assessment can document technical safeguards. A business owner can sign off on the intended use. Yet these records can sit in separate systems, describe different versions of the deployment, or rely on assumptions that are never written down.

The result is a deceptively simple problem: an organization may have completed its approval process without preserving a coherent account of the decision it actually made.

A deployment approval should not be treated as a folder of completed documents or a final signature on a launch form. It should be a record of a decision, supported by evidence and bounded by explicit conditions. That distinction changes what organizations need to capture before release.

The missing part of AI deployment approval: What makes the approval valid?

Consider a hypothetical financial services company preparing to deploy an AI assistant that reviews customer documentation and recommends whether an application is ready for further processing.

The system has passed its evaluation. The security team has reviewed the integration. The business owner has approved the use case, and human reviewers are assigned to check its recommendations. The deployment is approved.

But what exactly did that approval cover?

Was the system approved to review every category of customer document, or only a defined set? Was it evaluated on complete applications, or also on incomplete and contradictory submissions? Does the approval assume that a human checks every recommendation? Can the system continue operating if the review team changes its procedure or if a new data source is introduced?

These are not minor administrative details. They define the circumstances in which the original evaluation and risk assessment remain relevant.

An approval based on one set of conditions cannot automatically justify deployment under another. This is why a useful approval record needs something beyond system details, test results and signatures: it needs to preserve the boundary of the decision.

What an AI deployment approval record should contain

Most organizations already recognize the need for an AI inventory, technical documentation, security reviews, risk assessments and named owners. These remain important. The following structure focuses on connecting those records to the actual decision to deploy.

1. Define the exact use that has been approved

Start with the business activity, not just the name of the AI application.

A system may be described as a customer-support assistant, document reviewer or fraud detection tool. Those labels are too broad to establish what it is authorized to do. The approval should specify:

  • The business process in which the system will operate.
  • The precise tasks it may perform.
  • The outputs it may generate or recommend.
  • The decisions that remain exclusively with authorized employees.
  • The users, customers or other groups who may be affected.
  • The actions or use cases that are explicitly outside its approved scope.
For example, an AI system may be approved to identify missing fields in an application, but not to reject the application or communicate a final decision to the customer. That distinction should be visible in the approval record, not left to an informal understanding between the implementation team and business users.

2. Link the approval to the evidence that supports it

A statement that a system has passed testing is not the same as evidence that it is suitable for the intended use. The approval record should point to the actual supporting material. Here are the evidence area and what the approval should be able to establish:
  1. Functional evaluation: Which representative tasks and test cases were evaluated, and what results were obtained?
  2. Data suitability: Were the input data and reference materials appropriate for the intended purpose?
  3. Security and privacy: Which reviews were completed, and what limitations or outstanding actions remain?
  4. Human oversight: Was the proposed review arrangement tested and shown to be workable?
  5. Operational readiness: Are the required integrations, access arrangements, support and fallback processes in place?
  6. Risk assessment: Which material risks were identified, mitigated or accepted?
The important detail is traceability. Each material conclusion should be connected to the assessment, test result, approval or other evidence that supports it. If the approval says that human review reduces the risk of incorrect recommendations, the organization should be able to identify the review procedure and the evidence supporting that conclusion.

If it says that the system performs adequately on a particular class of documents, it should be possible to locate the evaluation that tested those documents.

A reviewer should not have to reconstruct the justification from a collection of unrelated attachments.

3. Record what the organization has chosen to accept

Testing does not eliminate every risk. A system may meet its performance target and still produce errors, struggle with unusual inputs or require human intervention in particular circumstances. The approval should not hide these limitations behind an overall score. For every material residual risk, record:
  • What can still go wrong?
  • Under which conditions is the failure plausible?
  • Who or what could be affected?
  • What mitigation is in place?
  • What risk remains after mitigation?
  • Who has the authority to accept that remaining risk?
This last point is particularly important. A technical team may establish that an error rate is within the evaluation threshold. It does not automatically follow that the business has accepted the consequences of those errors.

For example, an AI assistant might be sufficiently accurate to identify missing documentation, but its occasional failure to recognize an unusual document could delay an application. The technical result and the business consequence are related, but they are not interchangeable.

The person accepting the residual risk should have the appropriate authority for the business process concerned. The record should distinguish between a technical recommendation, a risk assessment and the actual acceptance decision.

4. Document the conditions under which approval was granted

This is the part that ordinary deployment checklists often leave underdeveloped. 

An AI system is evaluated in a particular environment. Its performance and risk profile depend on factors such as the data it receives, the workflow in which it operates, the permissions it has and the way employees use its outputs.

The approval should capture the assumptions that materially influenced the decision. For example here are some approval assumption and what should be recorded:

  1. Input data: The permitted data sources, formats and relevant quality expectations
  2. Workflow: The process steps and hand-offs used during evaluation
  3. Human review: Which outputs require review, by whom and before which action
  4. System access: The approved integrations, permissions and available actions
  5. Operating limits: Known constraints, excluded scenarios and conditions requiring escalation
  6. Support: The team responsible for maintaining the deployment and addressing operational problems
These are not merely implementation notes. They are part of the justification for allowing the system to operate. Suppose an AI assistant was approved on the assumption that every recommendation would be reviewed by a trained employee. If the business later changes the process so that recommendations are automatically accepted unless someone intervenes, the original approval may no longer be sufficient.

The model might be unchanged. The conditions that made its use acceptable have changed.

A deployment approval should therefore record not only what was approved, but what had to remain true for that approval to make sense.

5. Make approval conditional, not indefinite

A signed approval is a decision made at a particular point in time. It should not become an unlimited authorization that survives every subsequent change in the deployment.

The organization should define the events that require the approval to be reviewed. These may include:

  • A material change to the model, application or underlying configuration.
  • A new data source or a significant change in input characteristics.
  • An expansion into a different business process or user group.
  • A change to system permissions or the actions it can perform.
  • A change in the human-review arrangement.
  • Evidence that actual operating performance no longer matches the assumptions used during evaluation.
  • A new legal, regulatory or contractual requirement that affects the deployment.
Not every software update needs a complete reassessment. The appropriate response depends on the significance of the change and its relationship to the original approval.

The important thing is to establish the review criteria before deployment, rather than deciding retrospectively whether a change was important.

An approval record should therefore include its review date, the responsible owner and the conditions that trigger reassessment. Where appropriate, it should also specify whether a triggered review requires additional testing, a revised risk assessment, a new business sign-off or suspension of a particular use.

This turns approval into a controlled decision rather than a one-time administrative event.

6. Preserve the decision itself, including its conditions

The final approval should bring the preceding evidence and decisions together. A useful record should identify:
  • The deployment being approved and its relevant version or configuration.
  • The intended use and explicit boundaries.
  • The evidence reviewed before approval.
  • Material limitations and residual risks.
  • The conditions attached to the approval.
  • Outstanding actions, their owners and completion requirements.
  • The individuals who reviewed and authorized the decision.
  • The date of approval and the next review point.
  • The events that would require the decision to be reconsidered.
It should also distinguish between three possible outcomes:
  1. Approved: The system can be deployed within the documented scope and operating conditions.
  2. Conditionally approved: Deployment is permitted only within specified limits or after defined actions have been completed. Those conditions should be explicit, assigned to owners and subject to verification
  3. Not approved: The evidence, controls or operating arrangements are insufficient to justify deployment at this stage.
A conditional approval should never become a vague way of postponing unresolved issues. If a condition must be met before the system goes live, the record should say so.

The practical artifact: An AI Deployment Acceptance Record

The six areas above can be brought together in a single decision record. This does not need to replace model cards, technical assessments, security reviews or regulatory documentation. Its purpose is to connect them. The following is a proposed template that organizations can adapt to their own approval processes (field and the information to capture):
  1. Deployment identity: System name, relevant version, configuration and deployment environment
  2. Business purpose: Intended workflow, permitted tasks and excluded uses
  3. Evaluation evidence: Test results, evaluation scope, limitations and supporting references
  4. Data and dependencies: Approved data sources, integrations, permissions and material assumptions
  5. Human oversight: Review responsibilities, decision authority and escalation arrangements
  6. Residual risks: Unresolved risks, mitigations and authorized risk acceptance
  7. Operating conditions: Conditions that must remain true for approval to remain valid
  8. Outstanding actions Required actions, accountable owners and completion criteria
  9. Approval decision: Approved, conditionally approved or not approved
  10. Authorization: Decision-makers, roles, dates and supporting sign-offs
  11. Reassessment criteria: Review date and events that require reassessment
The most useful addition is a short section titled Conditions of Approval. It could look like this:
  1. Deployment: AI-assisted customer documentation review
  2. Decision: Conditionally approved
  3. Approved scope: Identification of missing or inconsistent information in specified application documents.
  4. Human decision boundary: The system may recommend further review but cannot independently reject an application.
  5. Evidence: Functional evaluation, data suitability assessment and security review.
  6. Accepted limitation: Unusual or unsupported document formats may produce unreliable results and must be referred for manual review.
  7. Conditions: Trained employee review remains mandatory before the application proceeds.
  8. Reassessment trigger: Changes to the approved document sources, system permissions, intended use or mandatory review procedure.
  9. Accountable owner: Designated business owner.
This is an illustrative example, not a record of an actual deployment. Its purpose is to demonstrate how an organization can turn a collection of assessments into a decision that another person can understand and verify.

Why this matters beyond the launch date

The value of a deployment approval record becomes clearer when someone needs to examine the decision months later.

A business leader may ask why a particular AI system was authorized. An internal auditor may want to establish whether the required reviews took place. A compliance team may need to understand which safeguards were considered. A technology team may need to determine whether a proposed change falls outside the approved scope.

Without a connected decision record, each team may have to search through separate documents, emails, spreadsheets and ticketing systems.

Even when the evidence exists, the organization may struggle to establish how it relates to the decision.

This is not just a documentation inconvenience. It weakens the organization's ability to explain why the deployment was considered acceptable and whether the original basis for that decision still applies.

The distinction is also reflected in established risk-management guidance.

NIST's AI Risk Management Framework describes risk management as an ongoing process. Its Measure and Manage functions connect evaluation results with decisions about whether development or deployment should proceed, and with the continued management of AI risks. The framework is voluntary, but it offers a useful structure for organizations designing their own processes.

The EU AI Act makes lifecycle responsibilities more explicit for high-risk AI systems within its scope. Article 9 requires a documented and maintained risk-management system, while Articles 14 and 26 address human oversight and deployer responsibilities. These provisions should be interpreted according to the system's classification, the organisation's role and the applicable legal requirements. They are not a universal deployment form for every AI application.

The common operational lesson is that approval cannot be separated from the evidence, responsibilities and conditions that support the use of the system.

Questions to ask before signing off an AI deployment

Before approving a deployment, the review team should be able to answer these questions without relying on informal explanations:
  1. Can we identify the exact business use and the boundaries of the system's authority?
  2. Can we trace the approval decision to the evaluations and assessments that support it?
  3. Have we documented the material limitations and residual risks?
  4. Has an authorized business owner accepted the risks that remain?
  5. Are the human oversight arrangements practical, resourced and clearly assigned?
  6. Have we recorded the assumptions about data, permissions, integrations and workflows?
  7. Can we identify the conditions that would make the original approval insufficient?
  8. Do we know who is responsible for reviewing the deployment when those conditions change?
If these questions cannot be answered, the organization may have completed its technical testing without completing its deployment decision.

 From approval documents to continuous AI assurance

An organization does not necessarily need another lengthy approval form. It needs a reliable way to connect the information it already produces.

Evaluation results, risk assessments, technical changes, human decisions and evidence of completed actions should not become disconnected records that have to be assembled again whenever someone asks for an explanation.

This is where continuous AI assurance becomes relevant.
KlaritiQ is being built around the connection between AI initiatives, risks, evidence, ownership and decisions. The objective is to help organizations maintain a clearer account of what was assessed, what was approved, what changed and what needs to be reconsidered.

It does not replace specialist testing, security assessments, legal advice or authorized human approval. Those responsibilities remain with the relevant people and teams.

The principle is straightforward: an organization should be able to explain not only why an AI system was approved, but also whether the reasons for approving it still hold.

That is what makes a deployment decision defensible beyond the day it was signed.

This article provides general operational guidance, not legal advice. Regulatory obligations depend on the system, its intended use, the organization's role and the applicable jurisdiction.

What did you think?

Discussion (0)

Comments from visitors are reviewed before they appear. Sign in to comment right away.

No comments yet. Be the first to share a thought.

See where your company's audit readiness actually stands.

Get my free audit readiness assessment